01
HIPAA and HITRUST inheritance that reduces your workload
Aptible enforces infrastructure-level controls and produces aligned evidence, so teams don't have to design those safeguards or document how their infrastructure meets HIPAA and HITRUST requirements.
02
Dedicated, non-shared environments by default
Every environment runs on dedicated infrastructure, so teams don't have to design isolation boundaries or take on the risk that comes with shared runtimes.
03
Continuous audit evidence that survives change
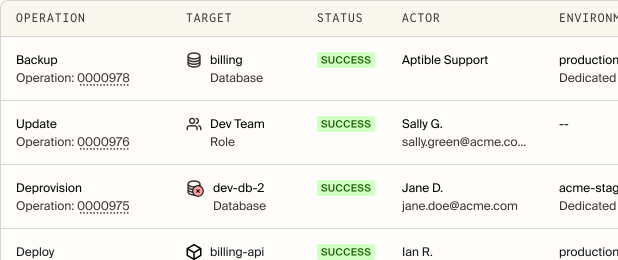
Infrastructure activity and access are captured automatically and retained over time, so evidence is already there when resources are rotated, rebuilt, or replaced.
04
One view of your HIPAA and HITRUST control coverage
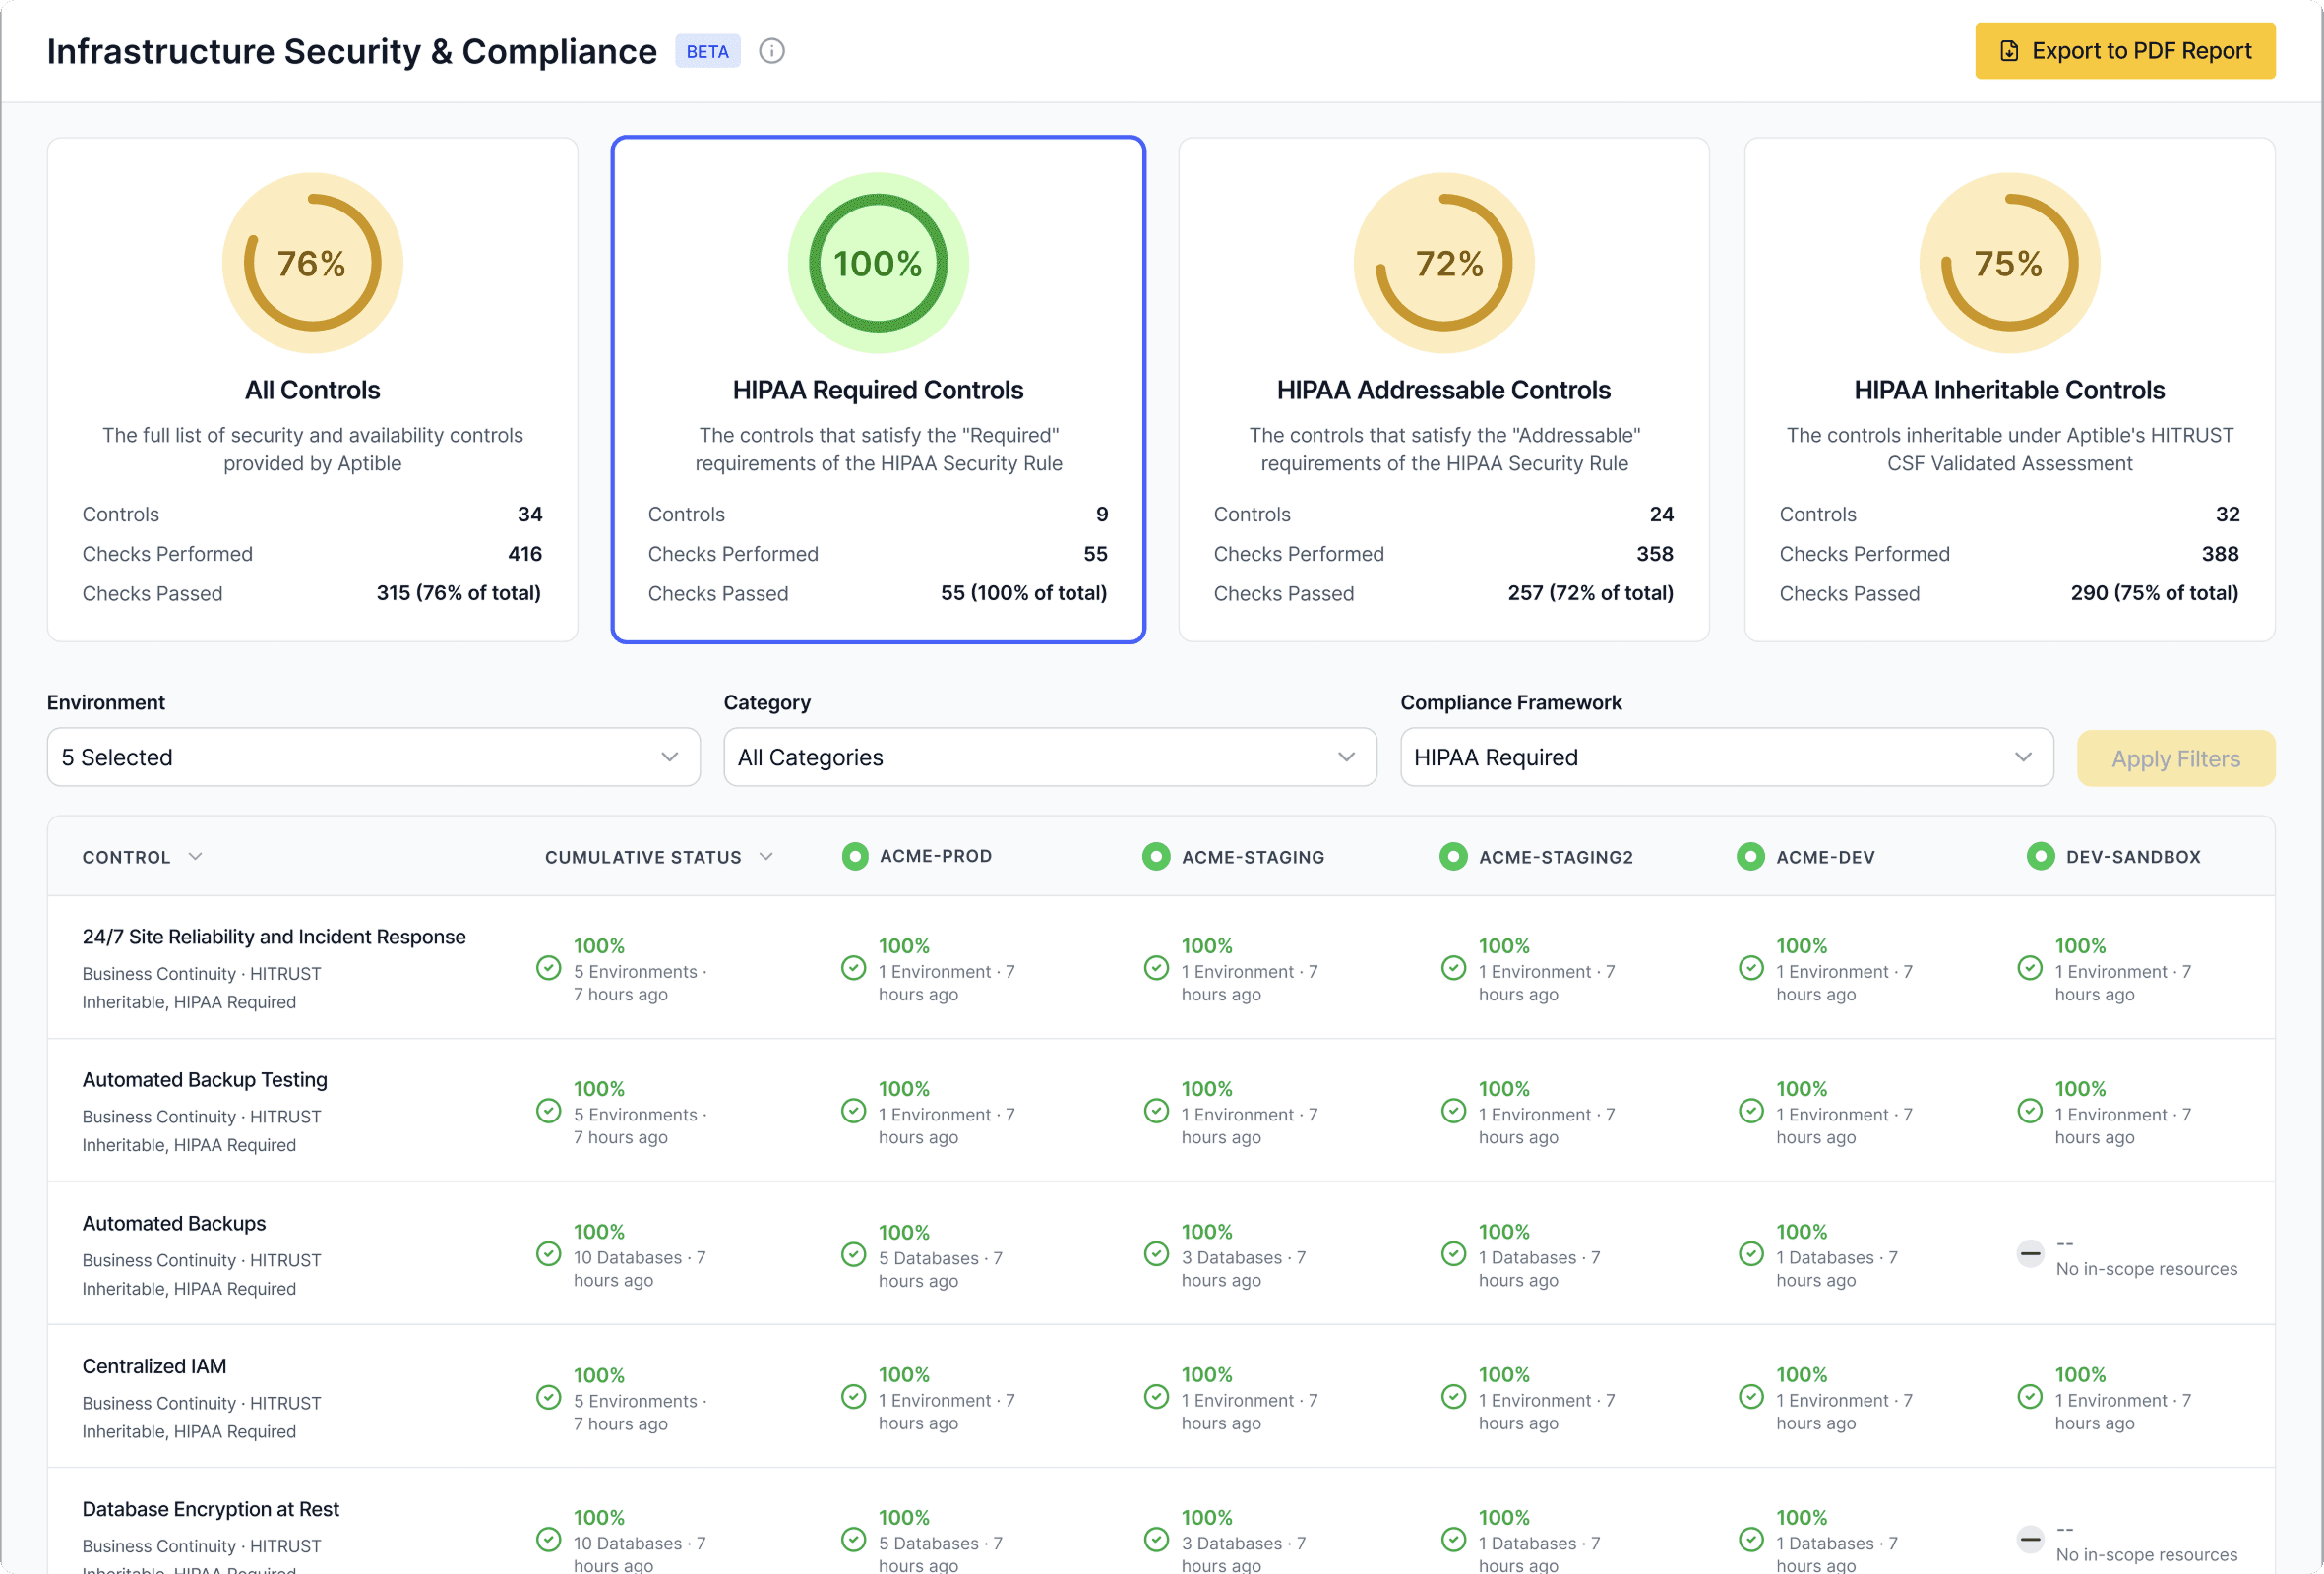
The compliance dashboard shows what's in scope, which controls apply, and what evidence exists for HIPAA and HITRUST, without manually assembling the picture.
05
Data residency and PHI-safe observability without extra BAAs
Aptible can retain logs and metrics within compliant infrastructure when telemetry may contain PHI, so teams don't have to route observability data to third-party vendors that require separate BAAs.
View docs
Compliance visibility built for audits
See what’s in scope for HIPAA and HITRUST, what controls are covered, and what evidence exists. Export audit reports without scraping logs, chasing screenshots, or rebuilding the picture before every review.
Shared responsibility, explicit and audit friendly
Aptible covers infrastructure isolation, encryption, platform access controls, audit logging, and evidence retention. You own application behavior and organization level policies and training.
Learn more
FAQs
Does using Aptible make my company HIPAA compliant?
No infrastructure provider can make your entire company HIPAA compliant on its own.
Aptible’s HIPAA documentation explains that Aptible automates and enforces 100% of the infrastructure security and compliance controls HIPAA requires on every resource in a dedicated stack: isolation, encryption at rest and in transit, platform access controls, audit logging, backups and retention, and continuous evidence generation. Aptible signs a BAA covering PHI processed in those environments.
Your company still owns application behavior and PHI handling in code, access control inside your app, organizational policies, workforce training, risk analysis, incident response, and vendor management. The Security & Compliance Dashboard shows which controls are covered and what evidence exists.
When do I need a dedicated stack and a BAA?
For apps and databases that handle PHI, you need a dedicated stack, available on the Production and Enterprise plans, plus an executed BAA. The HIPAA documentation explains that when you request your first dedicated stack, an Aptible team member coordinates the BAA. Shared stacks are for development, testing, and staging, and cannot host regulated data.
The LLM Gateway security and compliance documentation describes a separate coverage model: all LLM Keys are covered by an executed BAA, so you can send PHI through the gateway without a dedicated stack. Execute the BAA under Settings \> Agreements or right when you request a dedicated stack.
What's the difference between required and addressable controls?
HIPAA splits implementation specifications into required and addressable. Required means you must implement it. For example, 164.308(a)(7)(ii)(A) requires procedures to create and maintain retrievable exact copies of ePHI, which Aptible’s automated daily backups and retention policy satisfy.
Addressable means you assess it: implement the control, implement an alternative that accomplishes the same purpose, or document why it isn’t reasonable and appropriate for you.
Aptible’s HIPAA readiness documentation explains that in the dashboard, the HIPAA Required score is a binary indicator of whether you’re meeting the required specifications, and every resource on a dedicated stack meets them by default. The Compliance Readiness Scores documentation explains that the HIPAA Addressable score shows the percentage of addressable infrastructure controls you’ve implemented. You do not need 100% addressable before processing PHI.
Which controls do I inherit, and is there a mapping matrix for my auditor?
Aptible is HITRUST CSF certified. If you’re pursuing your own HITRUST certification, you can request that Aptible’s assessment scores be incorporated into your assessment through the HITRUST inheritance process.
The exact control split depends on your implementation and assessment scope. Aptible’s shared responsibility and inheritance materials are available through the HITRUST Alliance, and Aptible’s HITRUST CSF Validated Assessment Report and Letter of Certification are available in the trust portal.
For HIPAA, resources on a dedicated stack are configured to support Aptible’s HIPAA-eligible hosting requirements by default. The Security & Compliance Dashboard can help your team review required and addressable safeguards by environment and understand which responsibilities are covered by Aptible versus which remain yours.
Which frameworks is Aptible certified or attested for?
Aptible’s Security & Compliance overview describes support for SOC 2 Type II, HIPAA, HITRUST CSF, PCI DSS, GDPR, PIPEDA, the EU-US Data Privacy Framework, the Swiss-US Data Privacy Framework, and the UK Extension to the EU-US framework.
For your own SOC 2 or PCI assessment, Aptible provides the infrastructure controls and the evidence, and an independent auditor or QSA still assesses your organization.
Can I use Aptible instead of Vanta or Drata?
They solve different layers. Aptible provides secure infrastructure, enforced controls, and evidence for infrastructure-related requirements through features like the Security & Compliance Dashboard. Vanta, Drata, and similar tools manage the broader company compliance program: policies, employee controls, device posture, and audit workflows.
Some teams use Aptible alone for simpler HIPAA needs. Others use Aptible alongside a GRC tool for SOC 2, HITRUST, or a broader compliance program.
