Where fintech teams get burned
Once you’re storing financial data, security and auditability become part of your product
Fintech teams tend to ship quickly in the early days. Then a bank partner, enterprise customer, or auditor asks you to explain how your infrastructure actually works. Suddenly early architecture decisions become security liabilities.
Security reviews expose infrastructure shortcuts
Partners ask how production access is controlled, how infrastructure changes are tracked, and how environments are isolated.
SOC 2 preparation forces infrastructure cleanup
Audit preparation often reveals gaps teams postponed earlier. Logging coverage is inconsistent and access controls are broader than intended. Instead of documenting safeguards, teams end up rebuilding parts of their stack.
Bank and partner diligence slows integrations
Sponsor banks, payment processors, and financial institutions perform deep security reviews before approving integrations. Many require evidence that your infrastructure meets PCI DSS standards at the service provider level, even if you're not storing card data directly.
Infrastructure complexity grows faster than governance
Payments, ledgers, fraud detection, analytics, and dashboards all introduce new services and access paths. Over time it becomes harder to understand who can access production systems and where financial data flows.
AI tools introduce new financial data risks
Fintech teams are rapidly experimenting with AI for fraud detection, transaction analysis, and support automation. Without clear guardrails, sensitive financial data can end up flowing through systems that were never designed for regulated workloads.
Launch payments and transaction systems
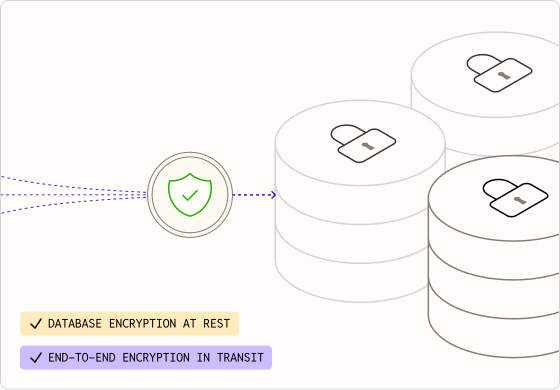
Run payment services, transaction processors, and customer APIs with encryption, isolation, access logging, and infrastructure guardrails enforced by default.
Pass partner security reviews
Answer diligence questions about infrastructure isolation, encryption, access controls, and operational history without reconstructing your architecture.
Operate ledgers and financial data systems
Run databases and ledger services with clear access boundaries and infrastructure activity history that holds up during PCI DSS assessments, SOC 2 audits, and partner security reviews.
Use AI safely with financial data
Route AI requests through controlled infrastructure with logging, credential management, and guardrails around how financial data interacts with models.
SOC 2 Type II and infrastructure controls
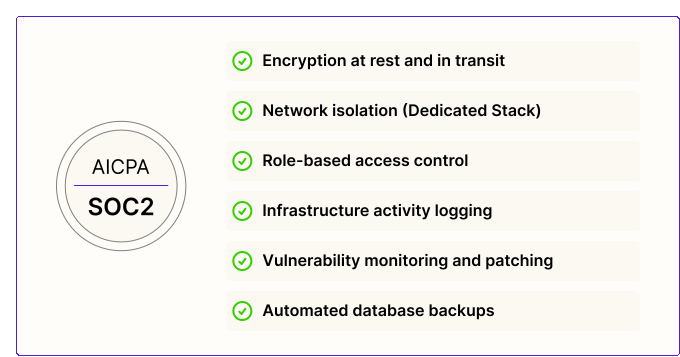
Most fintech startups pursue SOC 2 Type II at some point as they begin selling to enterprises and financial institutions. Many SOC 2 technical requirements relate directly to infrastructure behavior.
When deploying on AWS, teams must design and maintain these safeguards themselves. With Aptible, many of these controls are already enforced at the platform layer, reducing the engineering work required to implement and demonstrate them during audits.
Achieving soc 2 on aptible
PCI DSS and infrastructure compliance for fintech
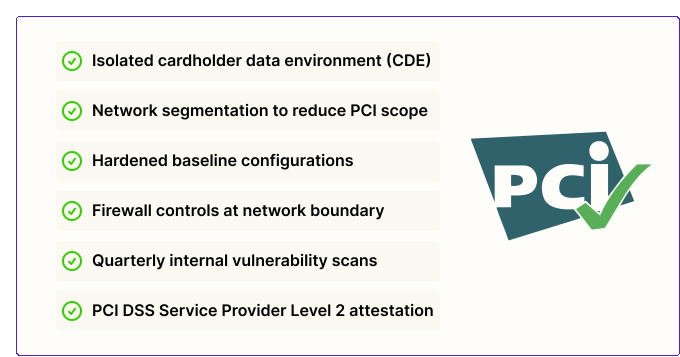
As fintech companies build payment infrastructure, pursue PayFac models, or integrate with sponsor banks, PCI DSS becomes a real requirement. Achieving it means demonstrating that your infrastructure meets a defined set of technical controls.
Aptible holds a PCI DSS Service Provider Level 2 attestation. When you deploy on a Dedicated Stack, Aptible enforces the infrastructure-layer controls required for PCI DSS compliance. The hardest part of your assessment is already handled: proving that the underlying platform is secure.
You still own your application layer. But instead of building PCI-compliant infrastructure from scratch on AWS, you inherit it.
achieving pci dss on aptible
FAQs
Is Aptible only for healthcare, or can fintech teams use it?
Aptible is not only for healthcare. Fintech teams use it for secure, audit-friendly infrastructure with enforced controls around isolation, encryption, access, logging, and operational reliability.
Aptible holds a PCI DSS Service Provider Level 2 attestation and a SOC 2 Type II attestation, and the same infrastructure controls described in Aptible’s Security & Compliance overview serve both healthcare and financial workloads.
Is Aptible SOC 2 Type II attested, and can I get the report?
Yes. The SOC 2 Type 2 Report and the SOC 2 Continued Operations Letter are available through trust.aptible.com after e-signing a mutual NDA. Request access with the email on your Aptible account.
For your own SOC 2, Aptible’s SOC 2 documentation explains that Aptible enforces the infrastructure controls auditors test, including logging, access control, vulnerability management, and encryption. The Security & Compliance Dashboard assists with evidence collection. An independent auditor still performs your assessment.
How can Aptible support PCI DSS readiness?
Aptible holds a PCI DSS Service Provider Level 2 attestation, available on request through trust.aptible.com, and enforces infrastructure-layer controls on a dedicated stack, including encryption, logging, access controls, monitoring, and evidence collection.
Your PCI scope still depends on your application, your payment flow, your cardholder data environment, your vendors, and your QSA’s interpretation. Plan packaging for PCI should be checked against the current pricing page.
How does Aptible help with sponsor bank or payment processor security reviews?
Aptible provides infrastructure security evidence for these reviews: the SOC 2 Type 2 report, the PCI DSS Service Provider Level 2 attestation, penetration test summaries, HITRUST materials where applicable, and shared-responsibility documentation, all through the trust portal.
Aptible also publishes guidance for working through security questionnaires and audits, and its Security & Compliance overview summarizes available compliance documentation.
What covers financial data contractually, since there's no BAA equivalent?
Financial data is covered by your customer agreement, data-processing terms, security commitments, and any applicable addenda, rather than by a HIPAA-style BAA. Aptible’s Terms of Service are the public starting point for contractual terms.
If you use AI workflows, Aptible’s LLM Gateway security and compliance documentation explains provider access, retention, and training restrictions for gateway traffic.
Can Aptible integrate with our existing cloud and data infrastructure?
Yes. Aptible supports mixed architectures through network integrations such as VPC peering and site-to-site VPN on dedicated stacks, so you can keep existing cloud and data systems in place while hosting regulated workloads on Aptible.
Aptible’s integrations overview includes supported integration patterns, Fivetran is available for data movement, and outbound IP addresses are published for allowlisting.
